Field noteAug 14, 20261 min read1 source

OpenAI Daybreak frames cyber capability as a controlled defense loop

Putting frontier cyber models in more trusted hands. Sources: OpenAI, OpenAI Stories.

In one minute

OpenAI primary-source post describes putting frontier cyber models in more trusted hands, indicating a concrete safety/access/governance change around high-capability cyber models. That is directly relevant to AI capability deployment and security policy. No prior coverage match is supplied, and the story has enough mechanism/consequence potential for a standalone if the post details access model, safeguards, and…

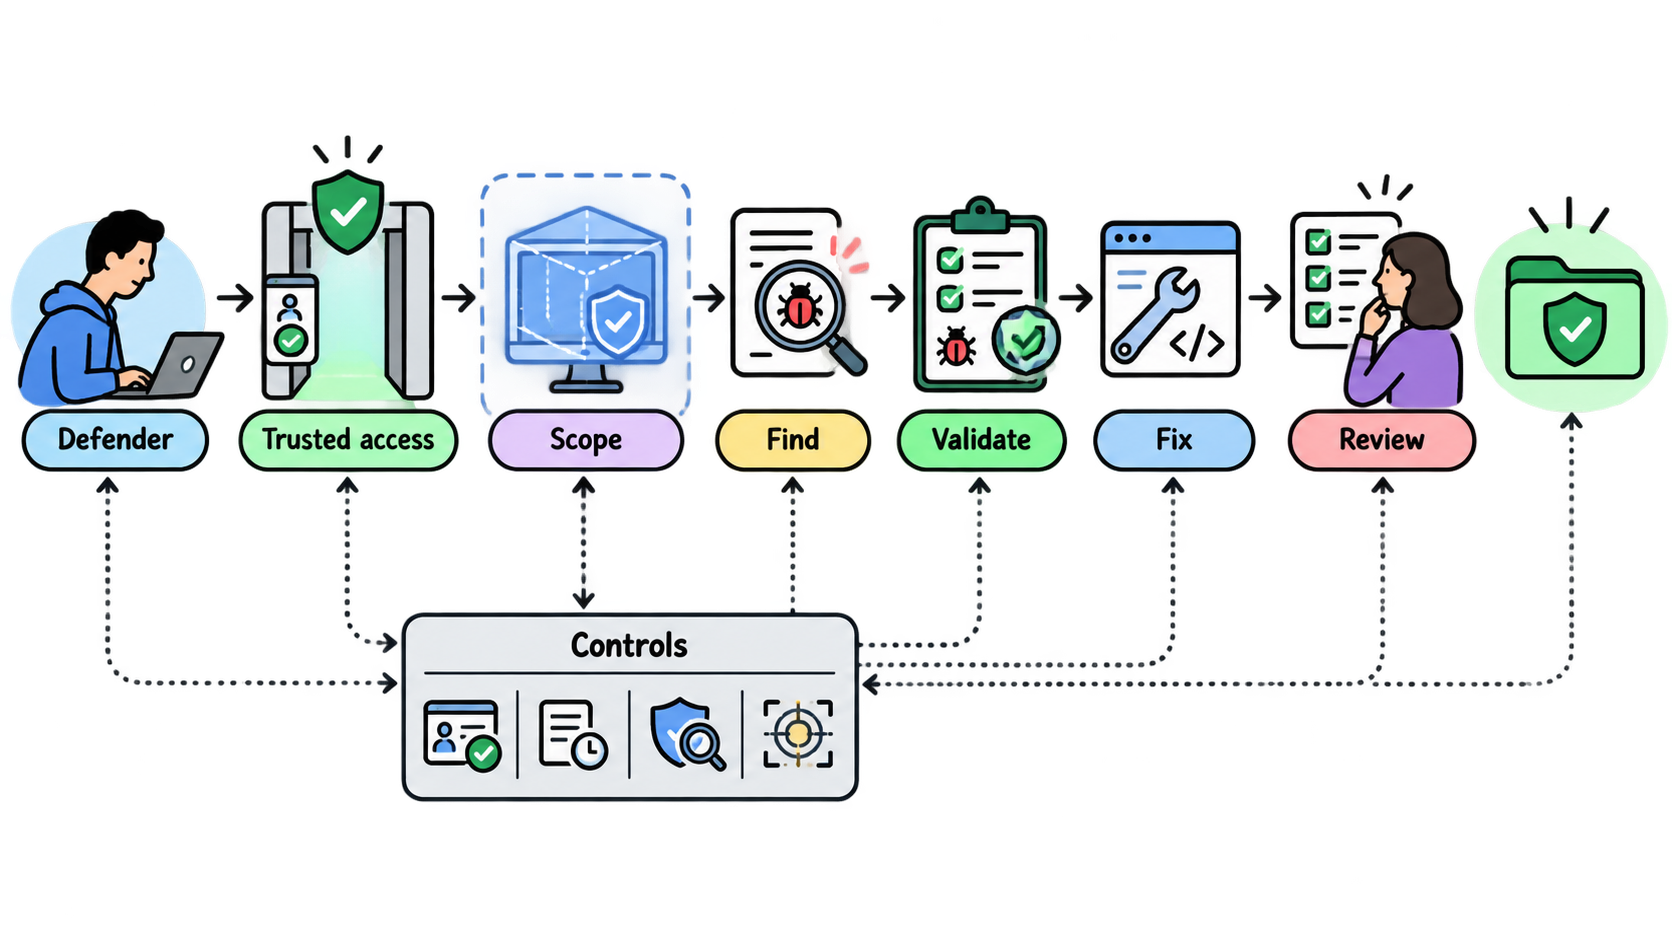
New Runtime synthesiseditorial-diagram
Diagram showing a defender passing through trusted access and scoped controls to find, validate and fix vulnerabilities before human review.
New Runtime synthesis: Daybreak frames cyber capability as a controlled remediation workflow rather than unrestricted model access.New Runtime synthesisOriginal source ->

Putting frontier cyber models in more trusted hands. Sources: OpenAI, OpenAI Stories.

Why it matters

OpenAI primary-source post describes putting frontier cyber models in more trusted hands, indicating a concrete safety/access/governance change around high-capability cyber models. That is directly relevant to AI capability deployment and security policy. No prior coverage match is supplied, and the story has enough mechanism/consequence potential for a standalone if the post details access model, safeguards, and recipients.

New Runtime view

Daybreak is governance architecture around a dangerous capability. Its runtime is a trust loop: eligible operators, scoped use, telemetry, feedback, and safety response.

Mechanism: A vetted access program gives trusted cyber partners scoped frontier-model assistance for defensive workflows.

Architectural boundary: Unrestricted cyber capability is separated from partner eligibility, monitoring, mitigation policy, and remediation use.

Measured consequence: The public consequence is a controlled channel for frontier cyber model evaluation and defensive throughput; no single reproducible benchmark is published.

What remains open

  • Partner gating can centralize benefits.
  • Dual-use leakage and operator misuse remain unresolved.
  • Public evidence is programmatic, not a full technical benchmark.

Sources

  • <https://openai.com/index/putting-frontier-cyber-models-in-more-trusted-hands>

Evidence / sources

  1. 1openai.com/index/putting-frontier-cyber-models-in-more-trusted-hands
All Field Notes

Next reads

Read next

Open the graph
  1. 01topicAiExplore the ai topic hub.
  2. 02topicSecurityExplore the security topic hub.
  3. 03topicModelsExplore the models topic hub.
  4. 04archiveField NotesOpen the latest editorial analysis.
  5. 05source ledgerSource LedgerInspect the public source evidence graph.
Who read this page?Machine requests, hidden until opened

Loading the privacy-safe route aggregate...

Open the JSON contract