Field note
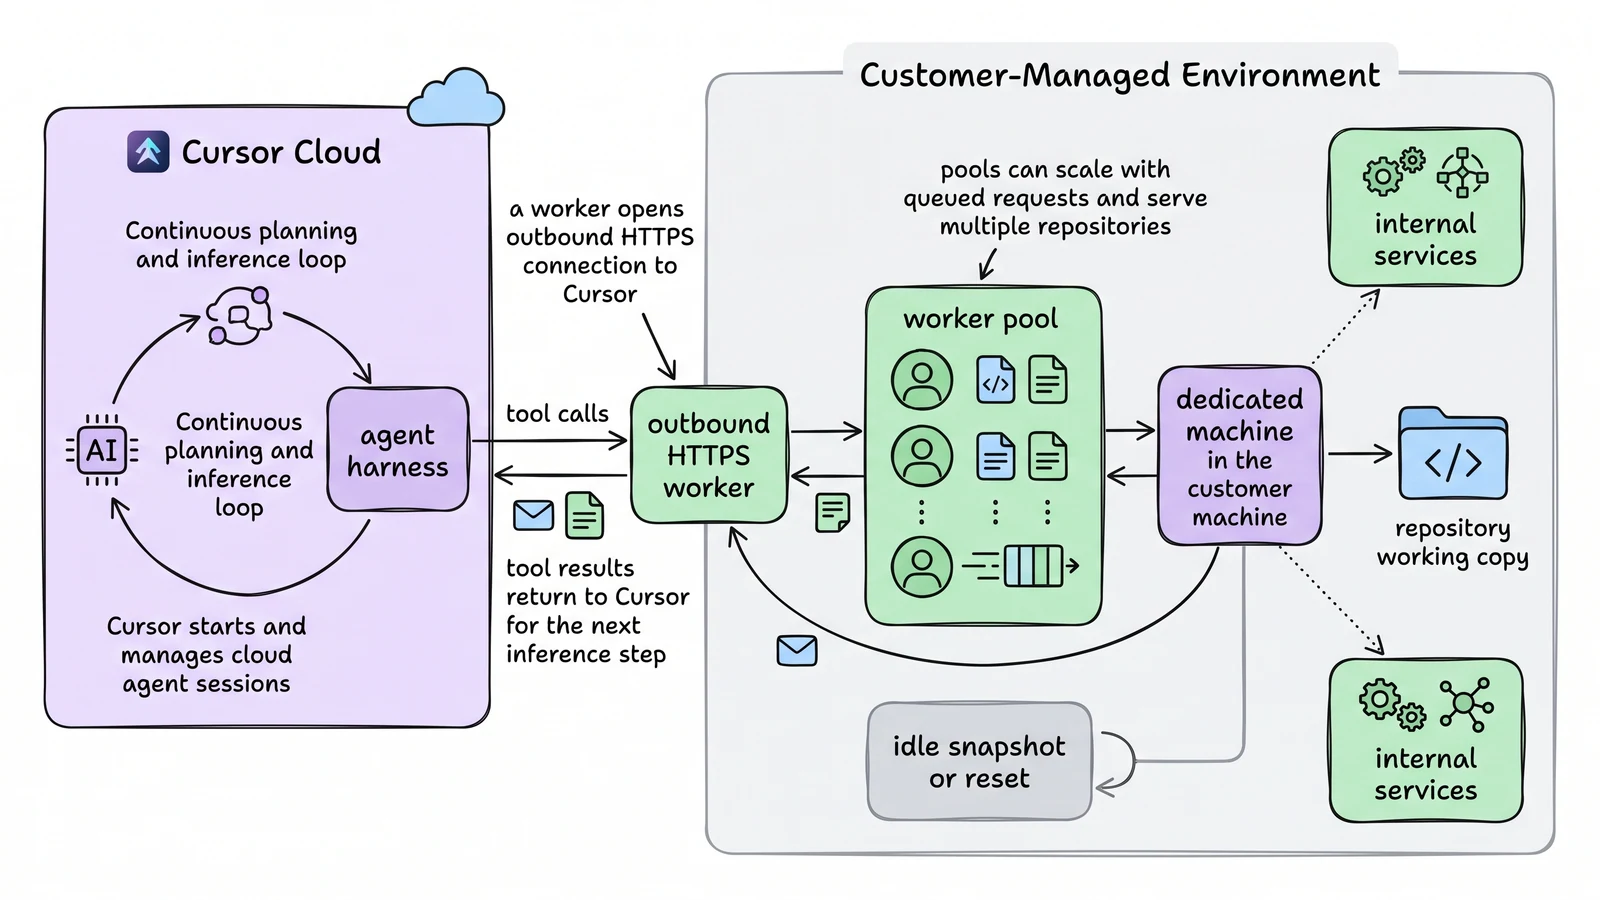
Cursor's self-hosted machines turn cloud coding agents into a split-runtime system. The source says agents are started and managed from Cursor, while execution can run on dynamically scheduled machines inside a customer's own network, close to internal services, source control, custom hardware, operating systems, and build pipelines.
The mechanism is an outbound worker bridge between customer infrastructure and Cursor's cloud agent loop. Cursor says the worker opens a long-lived outbound HTTPS connection, receives tool calls from the agent harness, runs commands against the local working copy, and returns results for the next inference step. Cursor also says it does not initiate inbound connections into the customer's network.
The immediate implication is that agent security moves from a simple cloud-versus-local choice into a split-control architecture. The evidence boundary is Cursor's product post; it describes the runtime design but does not prove customer deployment outcomes or incident rates. Watch whether self-hosted agent pools expose enough logging, transcript control, and data-retention controls for regulated engineering teams.