Cloudflare Adds a Network Enforcement Layer for MCP

Cloudflare combines protocol-level MCP detection, Portal-aware network policy, and server-side authorization into a layered enforcement model.

Retrieval answer

Cloudflare combines protocol-level MCP detection, Portal-aware network policy, and server-side authorization into a layered enforcement model. Cloudflare's MCP update makes the agent security boundary visible at the client, the network, and the server. Gateway with TLS inspection can classify conforming MCP traffic from protocol signals and expose the experimental.is_mcp selector in policy. Traffic Source metadata lets policy distinguish requests routed

New Runtime synthesiseditorial-diagram
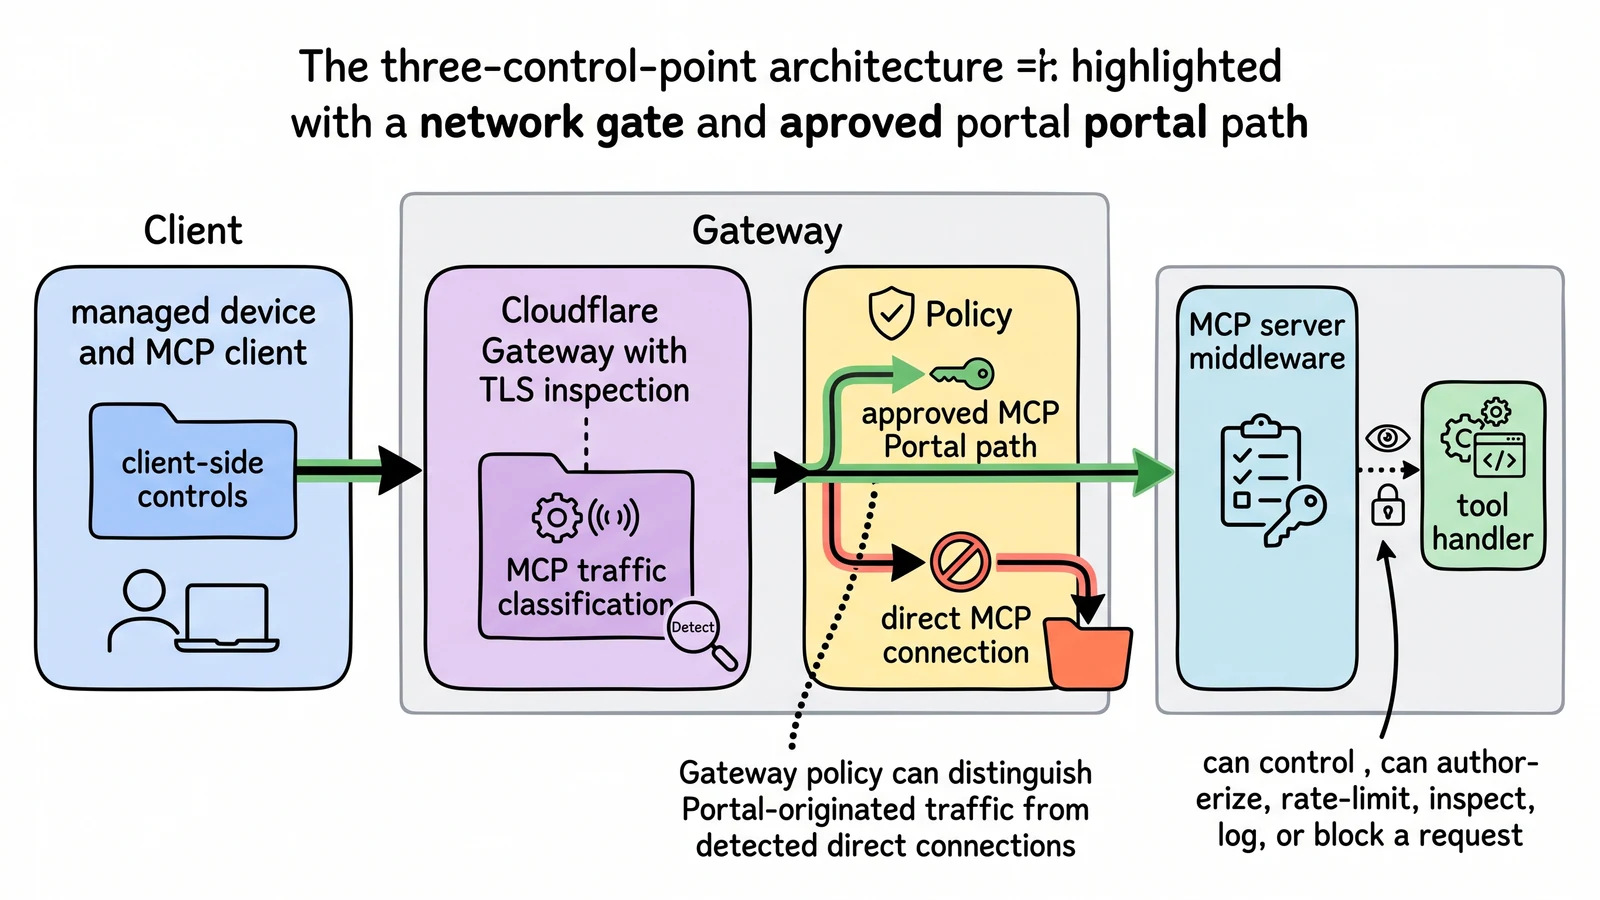
Whiteboard architecture map showing MCP controls in the client, at Cloudflare Gateway, and at the server, with Portal traffic allowed and detected direct connections blocked before tool execution.
New Runtime synthesis: MCP security becomes a layered path from client controls through network detection to server-side authorization before the tool handler runs.New Runtime synthesisOriginal source ->

Field note

Cloudflare's MCP update makes the agent security boundary visible at the client, the network, and the server. Gateway with TLS inspection can classify conforming MCP traffic from protocol signals and expose the experimental.is_mcp selector in policy. Traffic Source metadata lets policy distinguish requests routed through an MCP Portal from detected direct connections, while server middleware can still deny a call before its tool handler runs.

The mechanism is layered coverage: the network sees many remote connections, while clients and servers retain deeper context about the requested operation. This matters now because an employee can connect a coding harness to an MCP server with little friction and repeat a mistaken action at machine speed.

Security teams can begin with visibility, move approved servers behind Portals, and block direct managed-device paths without pretending the network replaces tool-level authorization. The evidence boundary is important: local stdio, off-network, Do Not Inspect, nonconforming, and undecrypted traffic can remain outside Gateway's view. Watch the selector's general-availability contract and whether tool-level reporting works across both known and shadow MCP servers.

Recommendation

Cloudflare combines protocol-level MCP detection, Portal-aware network policy, and server-side authorization into a layered enforcement model.

Discovery graph / next reads

Continue through New Runtime

Open the graph
  1. 01topicSecurity - New RuntimeExplore the security topic hub.
  2. 02topicAgents - New RuntimeExplore the agents topic hub.
  3. 03topicInfrastructure - New RuntimeExplore the infrastructure topic hub.
  4. 04archiveField NotesOpen the latest editorial analysis.
  5. 05source ledgerSource LedgerInspect the public source evidence graph.

These links are also published in this page's JSON twin and as typed edges in DiscoveryGraph v1.

Who read this page?Machine requests, hidden until opened

Loading the privacy-safe route aggregate...

Open the JSON contract